An SPF “too many DNS lookups” error means an evaluation exceeds the budget of 10 DNS-querying terms. The SPF check returns permerror: a permanent error, rather than a pass. Reduce the DNS lookup count by removing unused services or changing how you authorize legitimate senders. Retest the complete record after each change.
You can see your own lookup count in seconds with the free Rhycon email deliverability checker. This guide explains what is being counted and how to fix it.
What SPF actually checks
Sender Policy Framework (SPF) uses a DNS TXT record to identify servers authorized to send for a domain. Email receivers compare the connecting server’s IP address with that policy. SPF normally checks the envelope sender domain used for delivery, rather than the visible From address. DMARC connects that result with the visible sender through alignment.
A basic record for a Google Workspace domain looks like this:
v=spf1 include:_spf.google.com ~all
Each part has a job. v=spf1 marks it as SPF. include: pulls in another sender’s list. The ending (~all or -all) says what to do with anything not on the list.
What counts toward the 10 DNS lookup limit
RFC 7208 limits evaluation to 10 DNS-querying terms to constrain DNS work and reduce denial of service risk. The counted mechanisms and modifiers are include, a, mx, ptr, exists and redirect. The ip4 and ip6 mechanisms and all do not consume that term budget. The initial SPF TXT retrieval is not itself one of these terms.
The include mechanism can lead to nested records. DNS-querying terms in that evaluation share the same budget; nesting does not restart the count. The number of DNS lookups shown by a raw network trace is not a reliable substitute for this limit. Additional restrictions apply to address expansion and empty answers.
Most teams hit the limit by stacking tools: Google Workspace or Microsoft 365, a CRM, a marketing platform, a support desk, a billing tool and a cold email platform, all on one domain.
Why this matters for cold email
SPF permerror means the SPF policy did not produce a valid pass. It does not by itself prove that an email will be rejected: the receiver also considers other authentication and local policy. Gmail’s bulk-sender requirements include both SPF and DKIM, plus DMARC. Repair SPF rather than relying on another result to hide the error.
How to fix it
List every sender. Check your DMARC reports or your SPF record for every service that sends as your domain. Be honest about which ones still do.
Delete includes for tools you no longer use. Confirm the service no longer sends legitimate mail before removing its authorization.
Replace includes with IP ranges only if the vendor publishes stable ones. This is called flattening. It saves lookups, but if the vendor changes its IPs your record goes stale and mail starts failing. Avoid it for big providers like Google and Microsoft.
Move sending to subdomains. Send marketing from
mail.yourdomain.comand transactional fromnotify.yourdomain.com. Each envelope sender domain needs the correct SPF record. A subdomain can have a separate policy, but changing only the visible From address does not move the SPF check.Keep one record per domain. Two SPF records on the same domain is also a permerror. Merge them into one.
Keep each sending policy accurate and focused
Choose sending domains deliberately and authorize every legitimate service that uses the relevant envelope domain. A short Google Workspace policy may use v=spf1 include:_spf.google.com ~all when Google is the only sender. Add other services only when needed, then check the expanded result. Rhycon’s managed infrastructure uses Rhycon-owned domains and mailboxes for your outreach.
Other SPF mistakes worth checking
Using +all. This allows anyone on earth to send as you.
Using ?all. This tells receivers SPF is neutral and gives you no protection.
Record too long. A single TXT string is limited to 255 characters, so long records must be split into quoted chunks by your DNS host.
Too many void lookups. More than two lookups that return nothing can also cause an error.
Trace an SPF permanent error before editing DNS
Start with a received message and identify the envelope sender domain in its authentication results. Check that domain’s SPF record with your lookup tool. A checker pointed at the website domain may examine the wrong policy if your email service uses a separate return path.
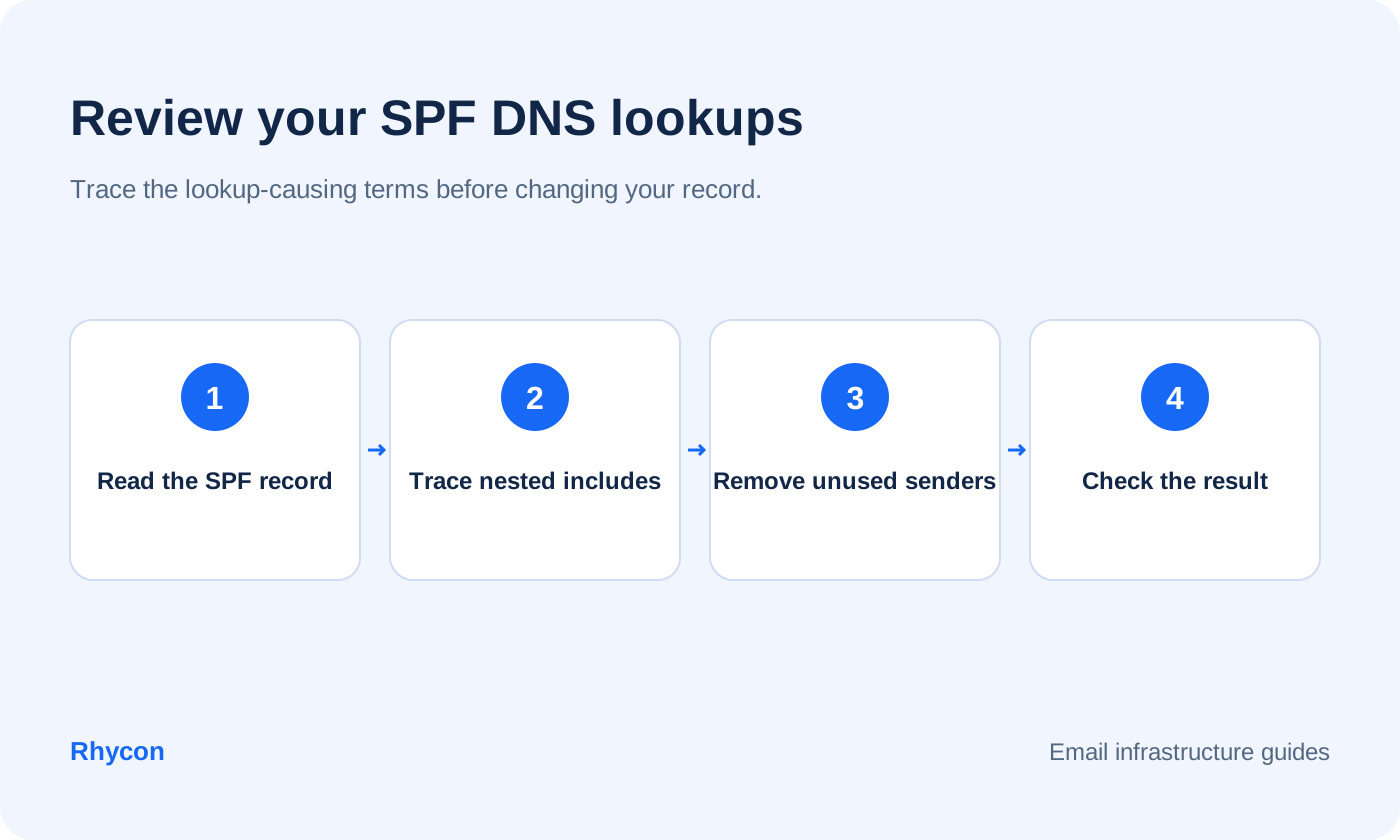
Write down each mechanism in the SPF record, then expand the services reached by include and redirect. Record the path that produced the error. This is more useful than counting only the includes visible in the top-level record. A short domain SPF record can still exceed its budget through nested dependencies.
For a simple illustrative example, suppose three services require three, four and four counted terms on the evaluated path. The total is 11, so it exceeds the limit.
If the first service is retired, removing its unused authorization can reduce that path to eight. Verify the real expanded policy rather than applying this example count to a vendor’s current records.
Reduce the number of DNS-querying terms with the smallest justified change.
Keep a copy of the previous record, note the responsible owner and verify delivery from every active sender afterwards. Treat DNS lookups errors reported by a checker as the start of diagnosis; confirm whether it found excessive terms, multiple records, invalid syntax or an empty lookup.
Use SPF record flattening only with an update plan. Explicit IP ranges can reduce DNS-querying terms, but they transfer maintenance to you or the flattening service.
Check who updates the ranges, how changes are detected and how failures are reported. A lower displayed count is not enough if the record no longer authorizes the servers that actually send your mail.
For the exact SPF specifications and limits, read RFC 7208. For Microsoft 365, use the provider’s current configuration guidance.
Provider reference: Microsoft’s SPF configuration guide explains how to identify and authorize your sending sources.
Check your record now
Paste your domain into the email deliverability checker. It reads your SPF record, counts the lookups, and flags the common mistakes above. It also checks DKIM, DMARC and MX, which you can read about in our guides to DKIM, DMARC and MX records.
SPF lookup limit FAQs
What happens if SPF has more than 10 lookups?
Exceeding the 10-term budget returns permerror. Email receivers decide how to handle that result under their own policies. It is a configuration error to resolve, not evidence of an SPF pass.
Do ip4 and ip6 count toward the limit?
No. Only mechanisms that need a DNS query count: include, a, mx, ptr, exists and redirect.
Is SPF flattening safe?
It is safe for small, stable vendors if you keep it updated, and risky for large providers that change IPs often. Using subdomains is the safer fix.
Can I have two SPF records?
A domain that publishes SPF must not publish two separate SPF policies at the same name. Combine the authorized senders into one valid policy and retest it.
See how Rhycon works and complete the homepage onboarding to explore how research, outreach and replies fit your workflow.