A “DKIM record not found” error means a lookup cannot retrieve the expected public key. Confirm the selector and signing domain in a sent message, then check the exact DNS name and provider configuration. A signature may exist even when the receiver cannot find the key needed to verify it.
Start with the free Rhycon email deliverability checker. A missing result for a guessed selector does not prove that your actual mail lacks DKIM.
What DKIM verifies
DomainKeys Identified Mail (DKIM) lets a sending service sign specified headers and content with a private key. The receiver retrieves the public key through DNS. A valid signature establishes responsibility for the signing domain and integrity of the signed parts. DMARC also requires alignment with the visible From domain.
Find the selector and domain in a received message
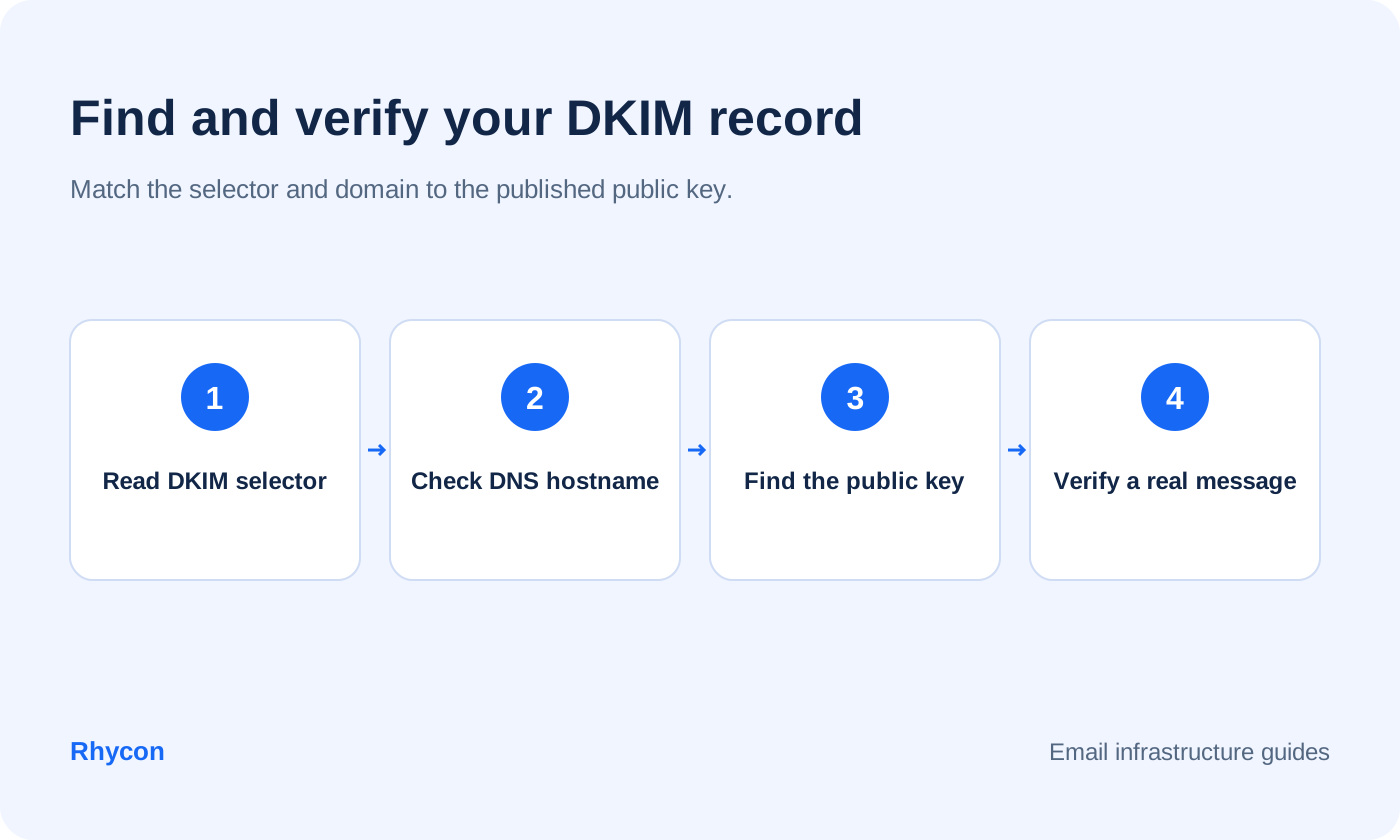
Open a message sent through the affected service. Read s= and d= in DKIM-Signature. If they are s=google and d=example.com, query google._domainkey.example.com. Use that exact combination rather than a selector copied from another account.
For a TXT-based setup, an administrator can run “dig TXT google._domainkey.example.com +short”, substituting the actual values. For Microsoft 365, check the selector’s CNAME and compare its target with the generated value in the Defender portal. Record the answer and lookup time.
Check these causes in order
Confirm the record type. Google commonly publishes a TXT record; Microsoft 365 uses provider-generated CNAME targets. Follow the actual sending service’s instructions.
Check the DNS name. Some DNS hosts append your domain automatically. Entering the full name in that interface can produce a duplicated suffix.
Check the authoritative zone. A record entered at the registrar has no effect when another provider hosts the active DNS zone.
Compare the complete value. A truncated TXT key or incorrect CNAME target requires correction. Copy the provider’s current value rather than reconstructing an old example.
Enable signing in the mail provider. Publishing a key and activating DKIM are separate steps.
Allow for cached DNS answers and provider setup time. Compare authoritative and public lookup results before repeating the edit.
Verify the repair with a real delivery test
Send through the affected service to an external mailbox and inspect Authentication-Results. A DNS checker confirms publication; a received dkim=pass result confirms verification for that message. If the key resolves but the signature fails, investigate the reported result and whether the signed content changed.
DKIM can survive forwarding when the signed parts remain intact. Modified content can invalidate it. SPF can also be affected by forwarding. For DMARC, at least one passing method must align with the visible From domain. Gmail’s bulk-sender rules require SPF, DKIM and DMARC.
For alignment, see our DMARC policy guide.
DKIM record FAQs
Should I use a 2048-bit key?
Follow your provider’s supported key lengths. Google recommends 2048-bit RSA where supported. Follow the provider’s rotation procedure and retain required selectors while messages using previous keys still need verification.
Does finding a TXT record prove DKIM works?
No. Check the actual selector, signing domain and received verification result. A record at an unrelated selector does not validate your message.
Provider references: Google Workspace DKIM setup explains publication, activation and testing.
For generated CNAME targets, use Microsoft’s current DKIM guide.
For help operating the setup, explore Rhycon’s managed infrastructure.
See how Rhycon works and complete the homepage onboarding to explore how research, outreach and replies fit your workflow.