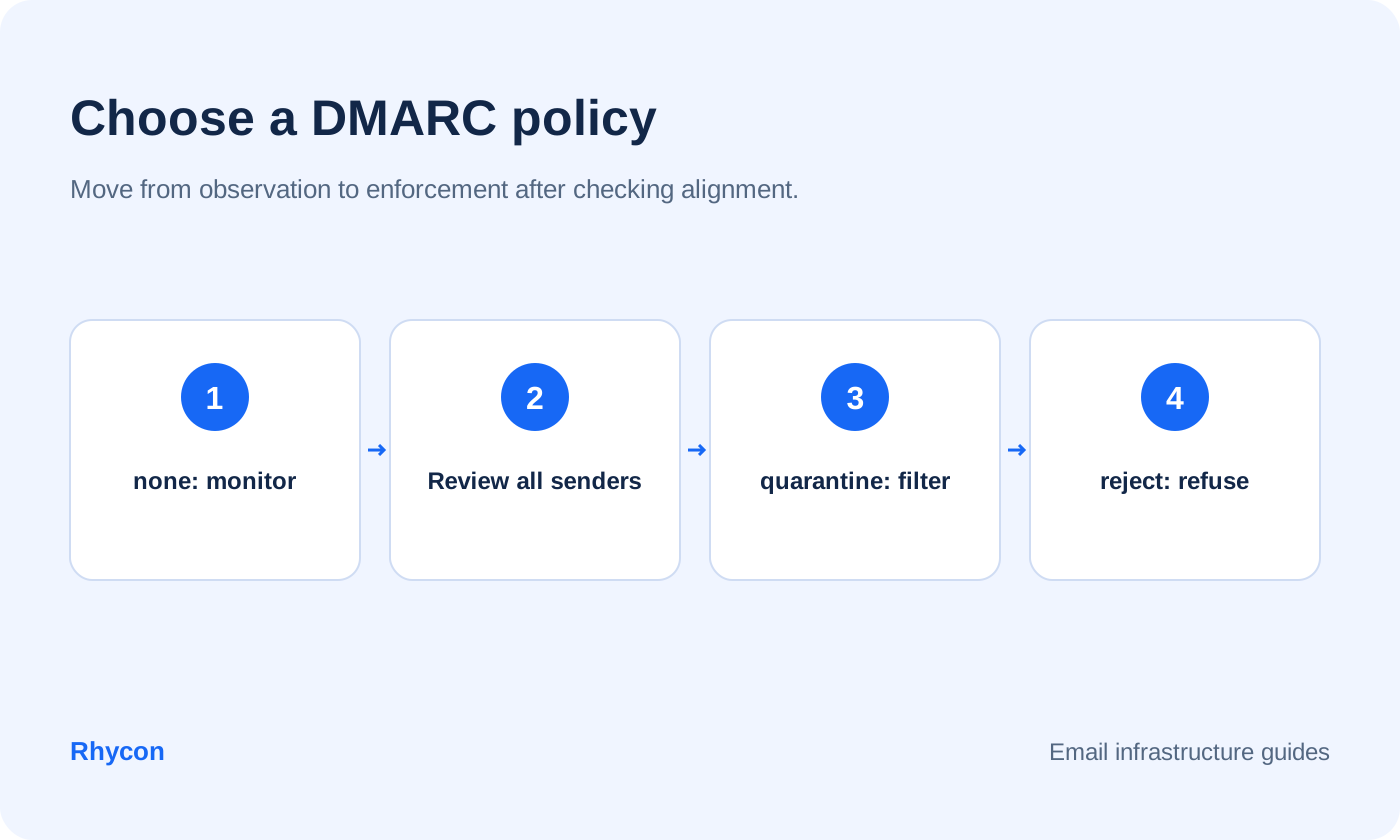
A DMARC policy requests how a receiving email server should handle messages that fail DMARC checks. The three DMARC policy options are none, quarantine and reject. For a new rollout, monitor your senders, fix alignment, then choose enforcement. Keep an existing working enforcement policy in place while you investigate changes.
To see what policy your domain has now, run it through the free Rhycon email deliverability checker.
What DMARC does
DMARC means Domain-based Message Authentication, Reporting, and Conformance. It uses SPF and DKIM results to assess the domain in the visible From address. At least one passing method must align with that domain. DMARC records also provide a way to request reports about observed email authentication.
The record is a TXT record at _dmarc.yourdomain.com. A starter record looks like this:
v=DMARC1; p=none; rua=mailto:dmarc@yourdomain.com
The three policies
p=none
The domain does not request DMARC enforcement. With a valid reporting address, you can review reports from participating receivers. Other filters can still block or route email to spam. A monitoring policy is useful for a new rollout; do not weaken an existing policy just to start collecting data.
p=quarantine
The domain requests special treatment for messages that fail DMARC, often delivery to the spam folder. Review legitimate senders before choosing this policy. The receiving service retains control over its final handling decision.
p=reject
The domain requests rejection of failing messages. This is a stronger enforcement request than quarantine, but receivers still apply their own policy. Validate legitimate mail streams before moving to reject so an alignment mistake does not disrupt expected correspondence.
Why this matters for cold email
Major mailbox providers publish authentication requirements for high-volume senders. Gmail requires bulk senders to use SPF, DKIM and DMARC, with a policy of at least none. Authentication does not guarantee inbox placement or permission to contact a recipient. Check the current requirements for the email services your audience uses.
How to roll it out safely
Publish p=none with an address that receives reports (rua).
Collect reports across a representative sending cycle. Use a DMARC report viewer to examine source IPs, authentication results and message counts. A fixed waiting period cannot prove that you found every sender.
Fix every legitimate sender that fails SPF or DKIM alignment.
Choose quarantine once you have reviewed the legitimate mail streams. The current DMARC standard removed the old pct sampling tag. Do not rely on pct=25 as a portable way to enforce a policy on exactly one quarter of messages.
Move to p=reject once you are confident.
Tags you will see
p: the policy for your domain.
sp: the policy for subdomains. If missing, subdomains inherit p.
rua: where aggregate reports are sent.
t: the current standard’s testing request. Check recipient and reporting-tool support before relying on it; it is not the old pct percentage.
adkim and aspf: strict (s) or relaxed (r) alignment. Relaxed is the default and is fine for most.
What to use on cold sending domains
For a dedicated cold sending domain, start at p=none with a report address, and move to quarantine once you know only your mailboxes send from it. Count every service that sends for the domain. Even a domain with a small number of mailboxes may also have web forms, billing or other automated senders. If you would rather not handle this for every domain yourself, see Rhycon’s managed infrastructure, which uses Rhycon-owned domains and mailboxes for your outreach.
Related guides: SPF lookup limit and DKIM record not found.
Read authentication results before changing policy
A message can pass an individual authentication test and still fail DMARC authentication. Open a received message and compare three identities: the visible From domain, the SPF envelope sender domain and the DKIM signing domain.
Use the receiver’s Authentication-Results header to see the outcome. Do not assume that a green SPF result alone settles the question.
Consider an illustrative message from sales@example.com. A service might use a return path at bounce.vendor.example and sign with d=vendor.example. If neither passing identity aligns with example.com, DMARC does not gain an aligned pass from those results. Configure the service to use an appropriate authenticated domain rather than simply replacing p=reject with p=none.
For a second example, a service signs legitimate emails with d=mail.example.com while the visible From address uses example.com. Relaxed DKIM alignment can accommodate related organizational domains. Strict alignment requires the same domain. Check the alignment mode in the policy and the actual received result before deciding whether a sender is configured correctly.
Keep an inventory of legitimate email services
List the systems that send emails for your organization: employee mailboxes, outreach platforms, support desks, billing services and website forms. Assign an owner to each one. Record its visible From address, return path and DKIM configuration. Include occasional senders that may be quiet during a short observation period.
Then compare that inventory with your aggregate reports. An unfamiliar source IP deserves investigation, but it is not automatically proof of an attacker. Ask whether it belongs to a service your team uses, a forwarded message path or an unauthorized sender. Keep the source, message count and authentication result together so the review has context.
An aggregate report groups observations; it is not an inbox placement report or a complete log of every recipient. Use it to investigate email messages and sending identities, then confirm a change with a real received test. Low volume or missing reports should prompt you to check reporting coverage rather than assume all mail passed.
Move from monitoring to enforcement with evidence
Before changing policy, test the routine mail streams and the less frequent ones. Send a normal invoice, support reply or form notification through its actual system. Save the receiving headers and confirm an aligned SPF or DKIM pass. A manual email from the employee mailbox does not test a separate application’s configuration.
For messages that fail DMARC, decide whether they are expected. Fix the authentication of legitimate senders and stop using services you no longer need. Keep unauthorized emails separate from configuration mistakes in the review. The policy decision should follow that investigation, not replace it.
Record the current policy before editing DNS and decide who will monitor the change. Watch delivery failures and reports after switching between quarantine and reject. If expected mail fails, diagnose the particular sender and alignment result. Avoid repeatedly changing the whole domain policy without identifying what happened.
Current-standard note: percentage sampling changed
RFC 9989, published in May 2026, replaced the earlier DMARC specification and removed pct. Its testing tag t requests different handling while a domain tests its policy. Deployment and tool support can differ, so review current provider documentation. Older guides that promise a precise staged rollout through pct may describe legacy behaviour.
Standards reference: RFC 9989. Use it for current DMARC policy and alignment definitions.
Provider reference: Microsoft’s DMARC setup guide explains domain configuration and reporting considerations.
For Gmail bulk-sender requirements, read Google’s email sender guidelines and check the policy that applies to your sending volume.
DMARC FAQs
Which DMARC policy should I use?
Start with none. Move to quarantine and then reject once your reports show all real senders pass.
Will p=none hurt my deliverability?
A none policy does not request DMARC enforcement. It does not guarantee delivery: a receiver can still reject or filter mail under other rules. Reporting also depends on a valid report address and receiver participation.
Do I need DMARC on every sending domain?
Yes. Each domain you send from should have its own record, or inherit one from a parent domain.
Why is DMARC failing when SPF and DKIM pass?
Check alignment. A passing SPF or DKIM result for an unrelated domain does not satisfy DMARC for your visible From domain. Review the envelope sender and DKIM signing domain, then configure the sending service’s domain authentication.
See how Rhycon works and complete the homepage onboarding to explore how research, outreach and replies fit your workflow.